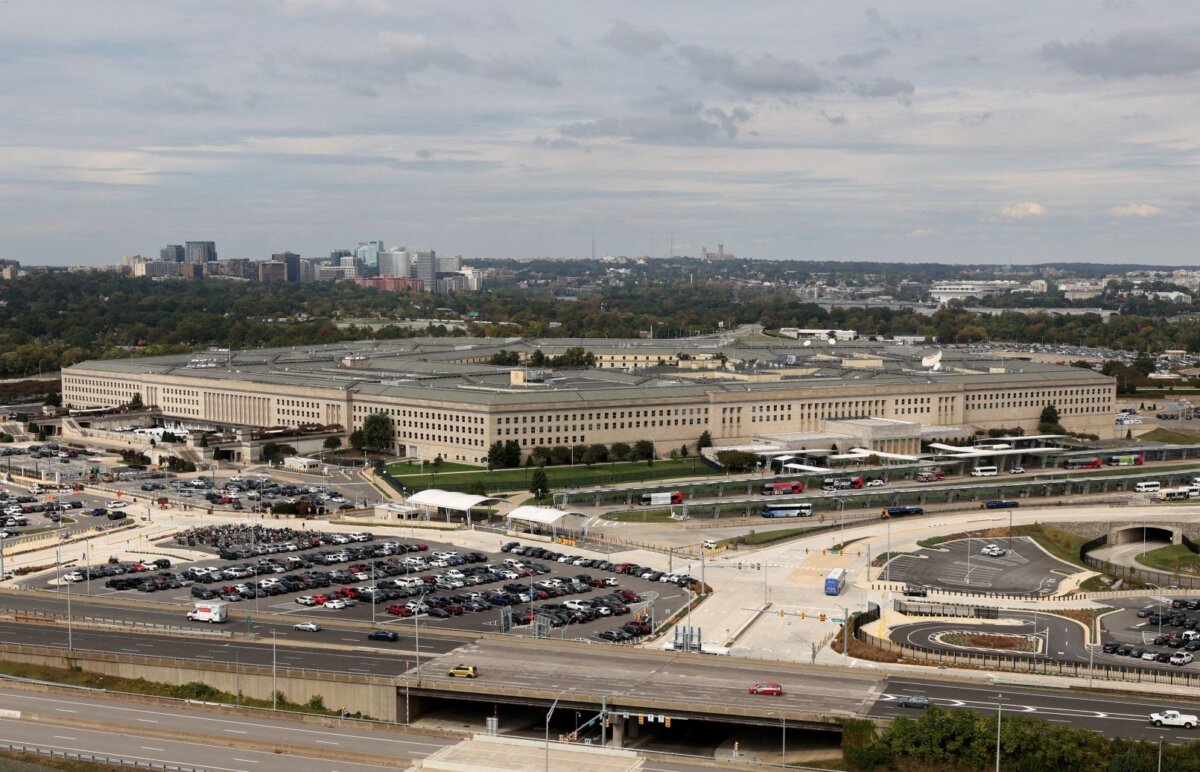
Pentagon’s personnel database had a breach that exposed the personal information of 2.76 million living people and another 294,000 deceased people, according to the Pentagon.
A small number of unauthorized users accessed the personally identifiable information on a Defense Manpower Data Center system between October 2025 and July 2026. The Defense Manpower Data Center immediately fixed the vulnerability upon discovering it. The Department of War said it doesn’t have any evidence that the stolen information has been misused.
The Defense Manpower Data Center on its website describes itself as the leader in information on Department of Defense human resource issues, personnel information, as well as entitlements, benefits, and medical readiness of uniformed service members, veterans, and their families.
Affected individuals are being notified by postal mail through the department’s contracted provider, Identity Theft Guard Solutions, known as IDX.
The FBI said in September it was investigating claims that cybercrime group ShinyHunters breached its employment website and obtained sensitive information about current and former agents and job applicants.
The FBI said Sept. 23 that investigators had not determined whether the alleged breach originated with a third-party provider or the bureau’s systems.
ShinyHunters said it targeted the FBI in retaliation for a May warning advising victims not to pay its ransom demands.
The FBI said Sept. 2 it was investigating a dark web site after reports it was selling more than 150 million U.S. and Canadian driver’s licenses, including license information belonging to the FBI’s assistant director.
Independent journalist Brian Krebs first spotted the marketplace, advertised on a Russian cybercrime forum, after his own Virginia license appeared as a free sample. He said nine people confirmed the scans were genuine. His record included front-and-back images plus infrared and ultraviolet versions, timestamped to a June 2025 flight.
The site, Nexus, claimed the scans came from an ongoing breach at a major identity-verification company serving Fortune 500 clients. It went offline after Krebs published. An FBI spokesperson confirmed the probe but declined further comment.
In 2015, the U.S. Office of Personnel Management disclosed that sensitive information, including Social Security numbers, had been stolen from background investigation databases, affecting 21.5 million people.
Those affected included 19.7 million applicants and 1.8 million others, predominantly applicants’ spouses or cohabitants. The records contained employment, education, residency, health, criminal, and financial histories, along with information about relatives and acquaintances. Some included fingerprints and findings from investigators’ interviews. Applicants’ usernames and passwords were also stolen.
A separate but related incident discovered in April 2015 involved stolen personnel data for 4.2 million current and former federal employees.
The U.S. Office of Personnel Management and the Defense Department announced plans to provide affected individuals with free credit monitoring and identity protection services for at least three years.
 Friends Read Free
Copy
Facebook
Tweet